



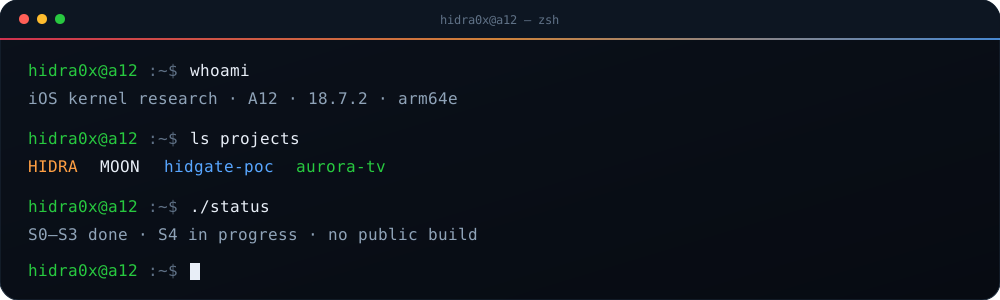
name: hidra0x
role: iOS kernel research
target: iPhone XR · A12 / T8020 · iOS 18.7.2
focus: AppleJPEGDriver CVE-2026-20687 → controlled free → double-free/write
strategy: data-only kernel control · no text patching · no fake PAC pointers
status: S0–S3 done · S4 in progress · no public build
I break things on a spare iPhone, read XNU at night, and write down every panic. The goal is not another crash — it is kernel control through data, not through a forged function pointer.
|
A12 / iOS 18.7.2 jailbreak research. Kernel entry via AppleJPEGDriver, then a data-only path to kernel r/w.
|
Open-source AppleJPEGDriver PoC: userclient, 0x58 ABI, deferred UAF, runnable IPA.
|
|
Kernel UAF research on 18.7.2/A12: IOHID crash-only, AppleJPEG controlled free, panic analysis, test matrix.
|
Lightweight Android TV launcher for Telefunken / Android 5–14. No ads, no trackers, no Google Play Services.
|
- RE:
AppleJPEGDriver 7.6.9,IOUserClient2022, queue / power paths. - Hunting: a double-free or write primitive from the stale
JpegRequestqueue node (S4). - Strategy: data-only —
proc,ucred,csflags, AMFI/MACF; no kernel text patching, no page tables unless required. - Next: KASLR leak after a write primitive; then PAC/PPL/KTRR-safe bootstrap.






«Паника — это не конец. Это доказательство, что мы уже в ядре.»
CRASH → CONTROL → JAILBREAK